Know what matters
See severity alongside signs of exploitation and the importance of affected devices. Understand why a finding deserves attention.
Your vulnerabilities are now our peasants.
We’re building ArxCura Intelligence to help you discover vulnerabilities across your network, understand which ones matter, and track what happens next from one cloud dashboard.
 ArxCura Intelligence
Sample data
Overview
Cybercriminals and state-backed groups are using AI to research targets and speed up their operations. When a new vulnerability surfaces, your team needs to quickly see what’s affected, know who owns the fix, and track it through verification.
Experience the future
ArxCura is designed to bring network scanning, prioritization, and follow-up into one workflow for IT and security teams.
Connect an ArxCura appliance to an approved network, or have a representative set it up.
The appliance is designed to find devices within your approved scan scope and run scheduled checks, with weekly scans as the planned default.
Sign in to a cloud dashboard that organizes results by device and priority and explains why each issue matters.
Assign work, keep a record of decisions, and compare follow-up scans to see what still needs attention.
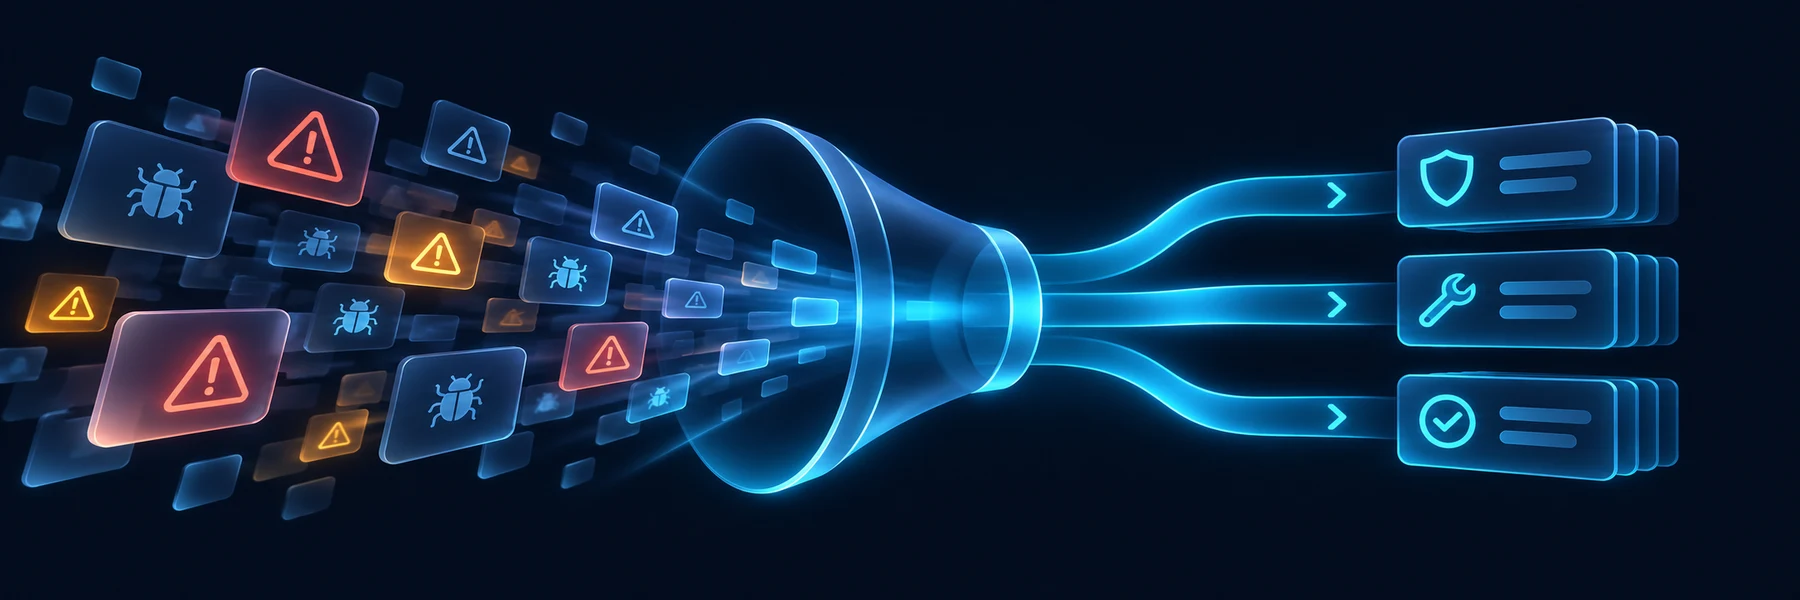
A scan is only the beginning. Which findings are urgent? Which share the same fix? Has the vendor already fixed the issue in your version? Did someone investigate it last month? Who owns the next step?
ArxCura is being built to turn scan results into trackable work. Keep the explanation, evidence, owner, and history together so each scan builds on the last.
We’re building tools to help teams prioritize findings, assign work, preserve evidence, and verify fixes.
See severity alongside signs of exploitation and the importance of affected devices. Understand why a finding deserves attention.
Group findings that share a fix and assign one work item to a person or team.
Record suspected false positives, vendor fixes, accepted risks, and investigation notes. Keep that context when a finding appears in a later scan.
See what’s new, what’s still open, who owns the work, and what a comparable follow-up scan verified.
Assignments and investigations are designed to live in ArxCura, with optional Jira synchronization for teams that already use it. Follow-up scans provide the evidence to verify fixes.
ArxCura is designed to combine scanner results with published vulnerability details, signals of exploitation, and the context your team records as work progresses.
Integrates scan findings and affected device details into one dashboard.
Published vulnerability details, severity scores, and references.
Estimates how likely a vulnerability is to be exploited.
Identifies vulnerabilities known to have been exploited.
Optional issue synchronization for teams that use Jira Cloud.
Have a question about what we’re building, or want to share how your team handles vulnerability monitoring?